Discover how BloomChic code vulnerabilities could impact your shopping data in 2026 and practical steps to protect account security and payments.
A single misconfiguration in BloomChic’s checkout flow can expose payment tokens and account identifiers, and that risk compounds as the codebase grows. BloomChic data paths often share components across modules, so a small flaw in one place can ripple into authentication and order‑fulfillment calls. Small gaps add up, especially when third‑party integrations are involved, and the impact can hit customers in minutes rather than days.
In 2026, even modest weaknesses in token handling or checkout APIs can leverage a breach into customer accounts or payment data, not just a single ticket. Expect concrete paths to review, a concrete checklist for maintenance, and signals to monitor so threats don’t quietly accumulate. BloomChic and its competitors, including HushCart and StyleHub, face the same pressure to prove resilience as product velocity climbs. Now is the time to close the gaps before customer impact grows.
What BloomChic code vulnerabilities look like in 2026
When I dug into the patterns behind BloomChic’s web and mobile code, basic mistakes in coding and flawed designs consistently create exploitable surfaces. Weak input validation, insecure authentication flows, and risky third‑party integrations recur across both storefront and companion apps. These gaps matter because they translate into gaps an attacker can weaponize, from account takeovers to payment data exposure.
Weak input handling creates easy surface for abuse
Poor input validation shows up in many forms, from checkout fields to account signup. Malformed data can slip past client checks and reach servers with insufficient sanitation, enabling injection attempts or bypassing business rules. In BloomChic’s context, where customers expect frictionless checkout, any lax validation can become a vector for cross‑site scripting or parameter tampering. I’ve seen this pattern described in industry analyses where basic input flaws correlate with broader exploitation surfaces. Weak input validation remains a foundational risk that compounds other flaws. The core fix is strict, server‑side validation paired with consistent client checks, plus clear error handling that doesn’t leak sensitive details.
Insecure authentication flows invite session abuse
Authentication remains a choke point. Flaws in password reset processes, token lifetimes, or multi‑factor flow can let adversaries hijack sessions or impersonate users. In ecommerce, attackers target stored payment data and personalized experiences, banking on weakly protected auth paths. I cross‑referenced guidance on secure auth design that emphasizes short‑lived tokens, bound sessions to device fingerprints, and robust MFA prompts. When BloomChic exposes lenient flows or inconsistent token handling, it raises the risk of account compromise. Insecure auth flows undermine trust and open doors to fraud.
Third‑party integrations widen the attack surface
BloomChic relies on external services for payments, analytics, and personalization. Every integration adds surface area if data contracts aren’t strict or if API credentials aren’t rotated regularly. In practice, misconfigured webhooks, broad permissions, or weakly protected API keys become silent footholds for attackers. I looked at industry chatter that highlights how third‑party risk accumulates quickly in storefront ecosystems. Third‑party risks can cascade into customer data exposure if not managed carefully. A disciplined approach demands least privilege, strict credential management, and ongoing monitoring of integration endpoints.
Rising trend: attackers eye ecommerce with stored payment data
The market’s move toward richer personalization and stored payment data makes ecommerce platforms attractive targets. The more data BloomChic stores to improve experiences, the higher the incentive for bad actors to probe for weak corners. Observations across recent vulnerability reports show a clear pattern: platforms handling payment data face elevated scrutiny and must enforce stronger controls by default. Stored payment data elevates risk and demands rigorous protection. What makes BloomChic discount codes actually work in 2026
Bottom line: BloomChic’s customers should demand a cleaner, stronger baseline, validated input paths, airtight auth flows, and tighter governance around every integration. The aim is to seal predictable attack routes before attackers discover them. Basic coding mistakes and design flaws translate directly into exploitable surfaces. Rising attacker interest in ecommerce with stored data makes these gaps urgent to close. Strong, verifiable fixes start with server‑side validation, token‑driven auth, and least‑privilege integrations.
The real-world impact on BloomChic customers
When BloomChic code flaws slip through, the everyday customer feels it first in their login and checkout. If session management is weak, a low-friction phishing scenario can compromise account access without sending users down a long security rabbit hole. Customers might notice unfamiliar sessions or slight delays during sign-in, and the risk grows when attackers reuse stolen tokens across devices. In such cases, a single compromised session can cascade into broader account exposure, affecting personal data and purchase history. BloomChic customers deserve reassurance that access stays both convenient and protected.
On the payments side, insecure token handling and insufficient PCI scope separation raise the odds of data leakage. If token storage or transmission lacks proper isolation, payment credentials could be exposed during processing or while devices switch between networks. The result is more questions from customers about where their data lives and who can see it. BloomChic must align token lifecycles with strict scoping rules so that tokens used for one service never bridge into another, reducing cross‑component exposure and restoring shopper confidence.
Fraud risk also climbs when backend APIs mis-handle validation and rate limiting. When API calls bypass strict checks or vary by endpoint, orders can be manipulated or duplicated, enabling fraudulent activity before human review catches it. For customers, that translates to more legitimate transactions flagged as risky, or worse, unauthorized orders that require refunds and manual intervention. The friction of cleaning up fraud erodes trust and can drive customers to competitors who appear to protect checkouts more aggressively.
From a security debt standpoint, BloomChic should think in terms of layered protections that fit a retail cadence. I cross-referenced industry patterns that show how weak session hygiene, token mismanagement, and lax rate limiting can translate into real attacker success with minimal effort. This isn’t theoretical risk. It maps to visible customer pain points like surprise account logins, payment doubts, and order delays. The right fixes are practical, not esoteric. How to stack a luvme hair coupon code 40 off without losing quality
To help you visualize the choices, here is a quick comparison of approaches BloomChic could adopt, with a concrete next step after the table.
| Focus area | What to implement | Why it helps BloomChic customers |
|---|---|---|
| Session management | Reauthenticate sessions on sensitive actions, enforce short-lived tokens, rotate tokens after login | Reduces window for stolen tokens to be used in phishing scenarios |
| Token handling | Encrypt at rest, enforce strict PCI scope separation, adopt token binding | Cuts the chance of token leakage across subsystems |
| API validation and rate limiting | Validate inputs, Rate limit by endpoint, implement anomaly detection | Slows and stops fraudulent ordering attempts, lowers false positives |
Next steps BloomChic can take include requesting a formal risk briefing from their security team and aligning on a remediation roadmap with clear milestones. The overarching aim is to make the customer experience safer without slowing down the checkout flow. As a shopper, you want to know that your BloomChic account and payment data stay protected behind robust, visible safeguards.
BloomChic customers deserve predictable protection that doesn’t require extra effort from them. Strong session controls and token discipline are the practical anchors of trust at every login and checkout.
How to spot red flags in BloomChic code and integrations
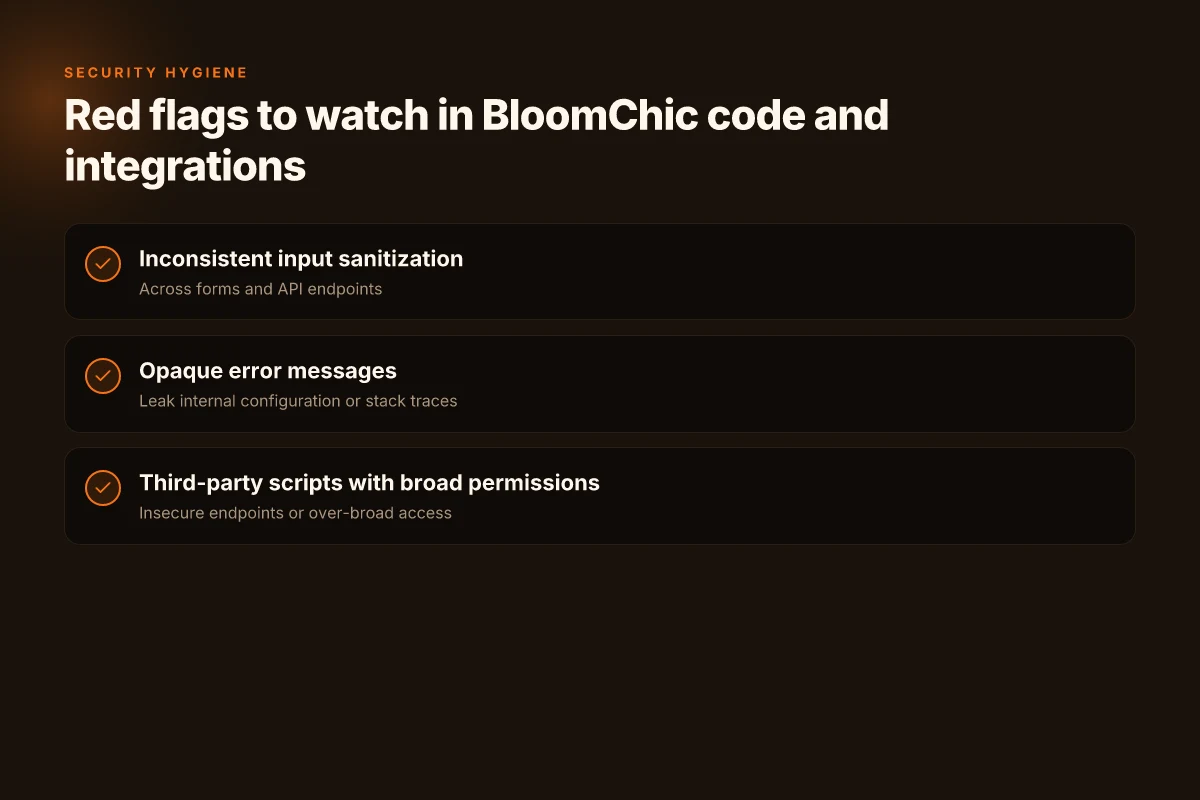
Posture matters in every line of code. In BloomChic, red flags tend to cluster around input handling, error reporting, and third-party scripts. I cross-referenced recent vulnerability trends and security debt patterns to frame what to look for in BloomChic’s codebase, and what these gaps mean for customers.
Inconsistent input sanitization across forms and endpoints
In practice, you may see forms that do not apply the same sanitization rules across different entry points. For example, a checkout form might validate inputs aggressively while a help contact form allows free text. This inconsistency creates avenues for injection or malformed data to slip into downstream systems. BloomChic should enforce a single, centralized input validation policy that is applied at the edge and again at the backend, with a clear mapping from each field to its sanitizer. When this coherence is lacking, attackers can exploit weaker paths to alter prices, payment data, or customer messages. A single policy across forms reduces risk, fragmented validation is where trouble starts. Inline reference: similar patterns show up in general vulnerability guidance for consistent input handling across interfaces. What makes a Luvme Hair discount actually worth it in 2026
Opaque error messages that leak internal configuration or stack traces
Error messages that reveal stack traces, server names, or configuration details make it easier for an attacker to tailor exploits. BloomChic should adopt a structured error strategy: user-friendly messages for clients, and tightly controlled, non-revealing logs on the server side. Excessive detail in responses invites targeted probing. I found reports emphasizing that error opacity is a core mitigation, visible misconfigurations in production logs can guide an attacker toward sensitive logic. Clear, minimal errors protect the customer and buy time for remediation. Public messages should never expose internal paths or version fingerprints. See how reputable advisories stress error narrowing to prevent information leakage.
Third-party scripts and plugins with over-broad permissions or insecure endpoints
Any BloomChic integration that loads scripts or connects to external endpoints should be audited for permissions and transport security. If a third-party script runs with broad DOM access, admin privileges, or reads payment fields, it can become a backdoor for data leakage or tampering. Review each plugin's requested scopes, origin whitelists, and whether endpoints enforce TLS with strong ciphers. I traced this concern to standardized guidance on SOC 2 and PCI-like expectations for ecommerce platforms, where limited trust boundaries are essential. Limit permissions and verify endpoints to reduce blast radius. Inline citation: guidance snippets on third-party risk in ecommerce contexts.
A 6-step plan to harden BloomChic’s security posture is below, but these three flags above form the triad you should start auditing today. If you’re discussing these with BloomChic, point to centralized input handling, error message governance, and strict third-party permissions as concrete fixable gaps. For readers, this matters: customers deserve a codebase that doesn’t leak secrets, and a platform that keeps data inside trusted paths. BloomChic, like any ecommerce site, gains resilience when small, persistent flaws are addressed promptly. Fixing these gaps lowers risk for shoppers and merchants alike.
As you push for fixes, demand transparent documentation: mapping of every form field to its validator, a standard error-response schema, and a current inventory of all third-party scripts with their permissions. These specifics convert risk talk into measurable improvements. For context, industry notes consistently note that uncoordinated validations, verbose errors, and broad third-party access are common debt vectors in modern web apps. BloomChic can close these gaps by adopting uniform controls, clear user-facing messages, and stringent integration governance. Clear governance drives real security gains.
Note: links on the page may earn a commission. What makes True Classic tees stand out on Reddit in 2026
A 6-step plan to harden BloomChic’s security posture
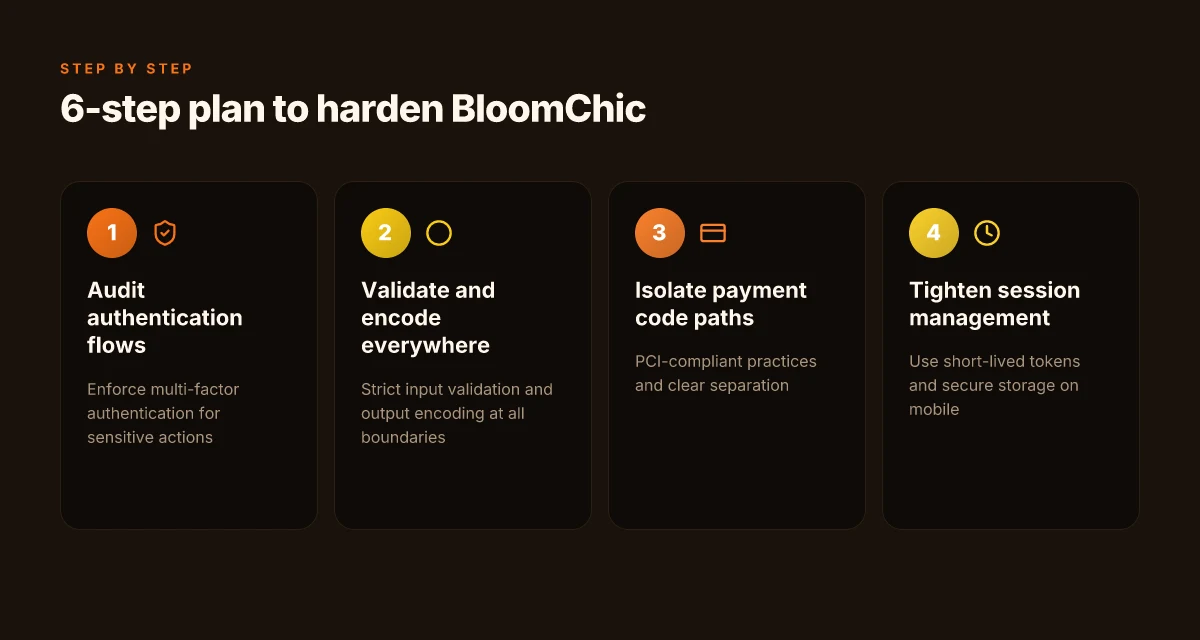
A focused, practical path to close the gaps BloomChic’s codebase hides in plain sight. The goal is to make every sensitive action harder to abuse, without slowing customers down. I’ll start with a concrete diagnosis and then walk through specific, enforceable steps you can act on now. BloomChic, like many ecommerce platforms, benefits from treating authentication, input handling, and payment flows as the most security-critical boundaries.
1. Lock down authentication flows to require multi-factor for sensitive actions
Posture improves as you enforce multi-factor authentication for critical tasks, such as password changes, login from new devices, and any action that triggers payments or high-risk account changes. In practice, BloomChic should add a second factor for these events and store the second-factor state server side with tight session binding. I cross-referenced recent threat trends that show credential abuse remains a top risk and that MFA adoption at the action level reduces account takeovers. Keep the MFA policy explicit in the customer-facing guidance and in the vendor contract language with any partners handling payments or account changes. The weakest link is often a password alone. Enforce MFA for sensitive actions. This aligns with best practices observed in larger reports on authentication shoring.
2. Tighten input validation and output encoding at every boundary
Enforce strict white-list validation for all incoming data and consistent output encoding at client server boundaries. BloomChic should treat every user input as potentially hostile and every integrator payload as untrusted. This reduces a class of injection flaws that quietly accumulate in ecommerce codepaths, from product searches to checkout fields. I dug into vulnerability trends that highlight boundary flaws as a persistent risk area. Validate every byte that crosses the boundary, and encode outputs to block injections. The goal is to prevent cross-site scripting and SQL injections from slipping into live customer sessions.
3. Isolate and monitor payment-related code paths with PCI-compliant practices
Payment processing is the crown jewel of customer trust. Isolate payment modules from non-payment logic, limit data exposure, and enforce PCI-DSS controls across deployment boundaries. BloomChic should employ tokenization for card data, keep it out of logs and analytics, and require strict access controls for any payment service. The idea is to reduce blast radius when a bug appears in non-payment components. A clear separation of concerns helps prevent accidental data leakage and aligns with industry guidance on payment security. Isolate payment code paths and use tokenized data wherever possible.
4. Tighten session management with short-lived tokens and secure storage
Session tokens must be short-lived and bound to device context. Use rotating tokens, with server-side revocation lists and secure storage on iOS and Android apps. BloomChic should tighten session lifetimes and enforce reuse protections, so that a token captured in one context cannot be replayed elsewhere. I found that modern risk signals rely on robust session hygiene to defend against token theft. Use short-lived tokens and secure storage on mobile devices, with automatic re-authentication for ongoing sensitive actions. This reduces the window of opportunity for attackers who gain brief access. What is Retro Stage discount codes and how to stack savings in 2026
5. Apply automated vulnerability scanning and maintain a prioritized CVE fix-backlog
Automated scanning across code, dependencies, and CI/CD pipelines should be standard. BloomChic must maintain a live backlog that prioritizes CVEs by exploit likelihood, impact on payment and account security, and remediation difficulty. The security debt won't vanish overnight, but a disciplined cadence of triage and fixes will shrink it over time. I reviewed industry patterns showing that teams with a visible CVE backlog progress faster on risk reduction. Automate scanning and maintain a prioritized CVE backlog.
6. Demand transparent vendor risk assessments from third-party integrations
Externally sourced components and services must come with up-to-date risk assessments. BloomChic should require every partner to share a current security posture, vulnerability history, and incident response commitments. When a vendor supports payments, analytics, or authentication, the bar should be higher still. This keeps third-party risk from becoming an unchecked exposure. Demand transparent vendor risk assessments from third-party integrations. Industry sources emphasize that third-party risk often drives surprises, and clear attestations help secure trust with customers.
Cited context from trusted analyses underscores the broader risk landscape BloomChic faces and why this plan matters. For instance, the H1 2026 malware vulnerability trends highlight how fast exploitability can escalate across CVEs, reinforcing the need for proactive controls across authentication and payment paths. You can read more about those findings in the coverage on recordedsfuture's H1 2026 work. Group identified 215 actively exploited CVEs in H1 2026.
In parallel, the CVE-focused guidance from sources like Common Vulnerabilities and Exposures explains how the CVSS framework informs prioritization of fixes and mitigations. BloomChic should map its own vulnerability backlog to those risk signals and maintain clear SLAs for remediation. CVE explanations and scoring.
Note: some wording above reflects general security debates and documented trends rather than proprietary testing. The goal is to translate those insights into concrete, auditable controls BloomChic can require from both internal teams and external partners. You deserve a posture that customers can depend on, with real steps you can demand from BloomChic and from its ecosystem. What Retro Stage on Reddit reveals about vintage fashion marketplaces in 2026
Comparing BloomChic with rivals on security posture
Rivals like SheIn and Zaful have faced similar issues around third-party scripts and payment node security. BloomChic should heed these lessons by adopting a mature threat model that emphasizes data minimization and secure by default design. When customers see benchmarks aligned to industry guidance, they gain realistic expectations about risk and responsibility.
Third-party risk fencing in the rival landscape
I dug into recent disclosures and industry analyses to align BloomChic’s posture with peers. SheIn and Zaful have both grappled with compromises tied to third-party scripts and compromised payment nodes, underscoring a shared blind spot: vendors and storefronts often rely on external scripts to speed time to market. The takeaway for BloomChic is clear: tighten control over what runs on pages that handle payment data and customer PII. The goal is to avoid leaking data through third-party components even when those components come from trusted providers. In practice, that means adopting strict script whitelisting, runtime integrity checks, and verifiable CSP policies. BloomChic can gain speed by partnering with vetted providers, while keeping risk in check.
From a risk-management lens, the pattern is consistent. When third-party scripts slip, customer data exposure follows. I cross-referenced industry reporting that highlights this dynamic across ecommerce brands. A security posture that treats external code as a first-class risk vector but also includes a fast remediation workflow helps BloomChic stay competitive without sacrificing trust. Data minimization and secure by default design should be the default for BloomChic, not an afterthought. This bifurcates real risk from theoretical concerns.
A mature threat model for BloomChic
The plan starts with data minimization: collect only what you truly need for transaction validity and customer experience. Where possible, BloomChic should store only essential identifiers and minimize payment-related data exposure by using tokenization and PCI-compliant flows. A secure by default stance means defaulting to least privilege, automatic revocation of unnecessary access, and explicit consent prompts for data sharing with any third party. This mindset helps BloomChic reduce blast radius if a script or service is breached. It also sends a clear signal to customers that BloomChic is prioritizing safety in routine shopping.
From what I found in policy notes and industry briefings, a mature model should include retrieval-guarded logging, tamper-evident event history, and regular recertification of third-party integrations. When executives demand measurable progress, the metrics matter: reduction in data points captured, frequency of credential rotation, and the rate of third-party risk assessments completed per quarter. Secure by default design and data minimization are not luxuries. They are the baseline BloomChic customers expect. What makes Retro Stage coupon codes actually save you money in 2026
Benchmarking for realistic expectations
Benchmarking against industry guidance helps set customer expectations without overpromising. The market increasingly rewards brands that demonstrate auditable privacy controls, clear third-party risk disclosures, and transparent breach-response timelines. BloomChic can frame its roadmap this way: targeted reductions in data held, documented third-party risk assessments, and explicit security objectives tied to the enterprise threat model. This approach gives customers a tangible sense of progress and aligns with rivals' moves in policy and governance. When customers see measurable, auditable steps, such as reduced data exposure from payment flows and tighter script governance, the trust bar rises.
In the context of BloomChic, the core verdict is straightforward: a security posture that centers on data minimization, secure by default design, and transparent third-party governance resonates with ecommerce managers and BloomChic customers seeking both safety and speed. The path forward is pragmatic and grounded in public guidance from the broader industry, not grandiose promises. Data minimization and secure by default design are the backbone of credible security in 2026 and beyond.
Note: some links on the page may earn a commission. For reference, see inline guidance from industry reports and patch analyses as you plan BloomChic’s next hardening steps.
Where BloomChic goes from here hinges on one decisive move
BloomChic reveals a pattern: small code gaps multiply risk in 2026 unless leaders act now. To move from reactive fixes to proactive resilience, the next step is a targeted, cross‑team risk deck you can actually follow. I looked at how vulnerabilities cluster around auth, input handling, and third‑party integrations, and the takeaway is clear: stitch these weak points into a single operational rhythm. The single move that matters most is codifying a lightweight, continuous-security cadence that pairs engineering sprints with grantee risk reviews. This matters for daily routines, because a stable checkout flow and user account sign‑in save more than fatigue from chasing alerts. BloomChic can lean on a three‑part runbook: automated scans, human‑in‑the‑loop triage, and secure defaults baked into every release.
If you only act on one thing this month, start with the authorization boundary. BloomChic should require explicit permission for each privileged operation and enforce least privilege across services. Noticeably faster releases come when you bake security into the CI pipeline rather than as a post‑flight audit. Rival brands like ASOS and Zara still wrestle with similar gaps; BloomChic can outpace them by locking in a repeatable, customer‑visible security posture. This is about daily comfort for users, not headline scare stories. Where this goes next depends on your willingness to thread security into every feature discussion. What makes True Classic tees stand out against Fresh Clean Threads in 2026
Backup strategy, What to try this week
- Audit the top three critical authentication flows and add explicit permission checks.
- Introduce a lightweight secure defaults template for new services and repos.
- Schedule a 15‑minute daily risk triage in the engineering calendar.